

How Sharing Works
When you share a project:- The project’s AES-256 key is decrypted on your device using your private key
- The key is re-encrypted (wrapped) with the collaborator’s RSA public key
- The wrapped key is stored on the server as a
projectSharerecord
Both users must have completed the password setup (encryption keys generated) before sharing is
possible.
Adding a Collaborator
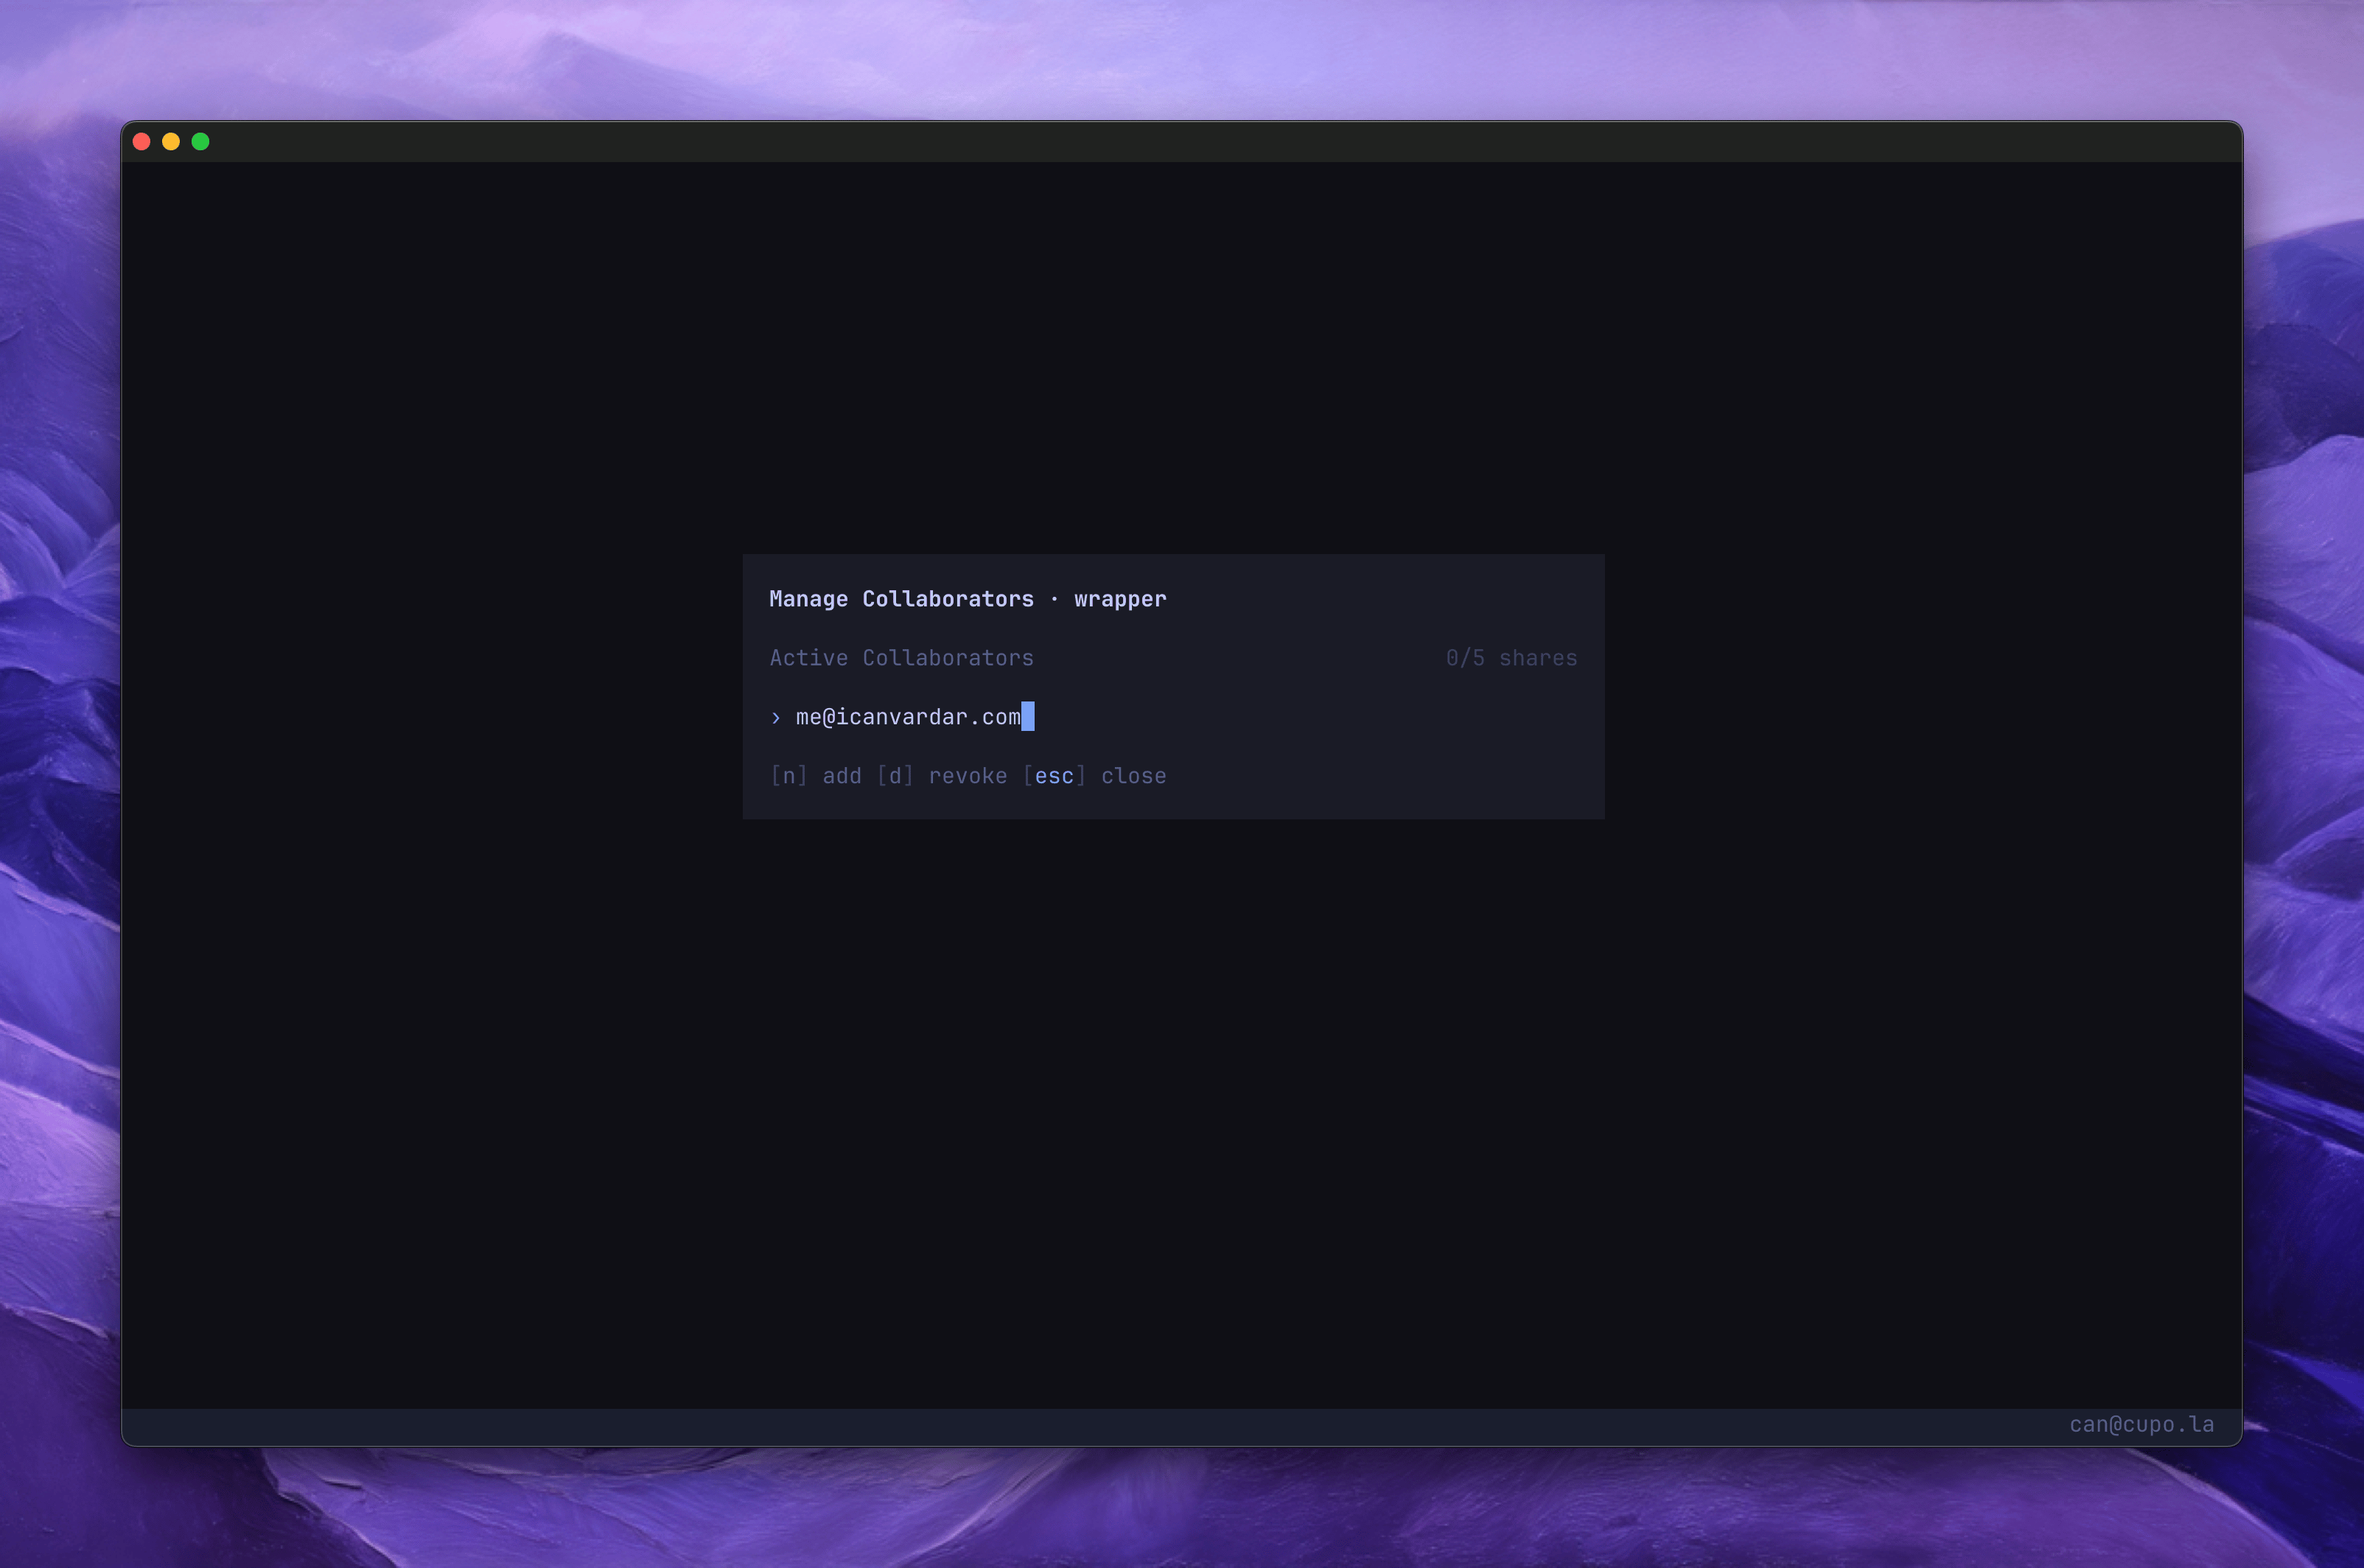
Open the TUI and navigate to any environment in the project:- Press
cto open the collaborator management modal - Press
nto add a new collaborator - Enter their email address
Revoking Access
When you revoke a collaborator, you have two options:Revoke only
The collaborator’s share is marked as revoked. They can no longer fetch secrets. However, they previously had access to the project key. Pressd on a collaborator, then y to confirm.
Revoke with key rotation
For maximum security, revoke with key rotation. This generates a new project key and re-encrypts everything. Pressd on a collaborator, then r to revoke and rotate.
1
Share revoked
The collaborator loses access immediately.
2
New project key generated
A fresh AES-256 key is created on your device.
3
Secrets re-encrypted
Every secret in the project is decrypted with the old key and re-encrypted with the new key.
This happens entirely on your device.
4
Remaining shares updated
The new project key is wrapped with each remaining collaborator’s public key.
5
Caches invalidated
The key version is bumped. All CLI caches are invalidated so the next
relic run fetches fresh
data.Permissions
Only the project owner can manage collaborators and archive the project.
Limits
Sharing requires the Pro plan. If you exceed the included shares, the TUI will prompt you to confirm the additional cost before proceeding.
See Security & Encryption for the full cryptographic details of how project sharing works.